
比特币白皮书早期草稿
首次公开证据
打开首次公开证据比特币:一种点对点的电子现金系统
Satoshi Nakamoto
www.bitcoin.org
摘要。 一种纯粹点对点的电子现金版本,将允许在线支付直接从一方发送给另一方,而无需承担经过金融机构的负担。数字签名提供了部分解决方案,但如果仍需要可信第三方来防止双重支付,其主要优势便会丧失。我们提出一种利用点对点网络解决双重支付问题的方案。该网络将交易哈希进一条持续延伸、基于哈希的工作量证明链,为交易加上时间戳,从而形成一份若不重新完成工作量证明便无法更改的记录。最长链不仅能证明所见证事件的先后顺序,还能证明它来自最大的 CPU 算力池。只要诚实节点控制着网络中的大部分 CPU 算力,它们就能生成最长链,并超越任何攻击者。网络本身只需要极少的结构。消息以尽力而为的方式广播,节点可以随时离开和重新加入网络,并将最长的工作量证明链视为自己离线期间所发生事件的证明。
1. 引言
互联网商业几乎已经完全依赖金融机构充当可信第三方来处理电子支付。尽管这一系统对大多数交易而言运作得足够好,它仍然受到基于信任模式固有弱点的困扰。真正完全不可逆的交易并不存在,因为金融机构无法避免介入争议。调解成本会增加交易成本,限制实际可行的最小交易金额,并切断小额临时交易的可能性;而更广泛的代价,则是无法再为不可逆的服务进行不可逆的支付。由于存在撤销的可能,对信任的需求便会蔓延。商家必须提防客户,纠缠他们索取原本并不需要的更多信息。一定比例的欺诈被视为不可避免而予以接受。面对面使用实体货币可以避免这些成本和支付的不确定性,但若没有可信第三方,目前不存在通过通信信道进行支付的机制。
我们所需要的是一个以密码学证明而非信任为基础的电子支付系统,使任何两个自愿的参与方都能直接彼此交易,而无需可信第三方。计算上难以逆转的交易可以保护卖方免受欺诈,而常规的托管机制也很容易实现,以保护买方。在本文中,我们提出一种使用点对点分布式时间戳服务器解决双重支付问题的方案,为交易的时间先后顺序生成计算证明。只要诚实节点共同控制的 CPU 算力多于任何相互协作的攻击节点群体,该系统就是安全的。
2. 交易
我们将一枚电子币定义为一条数字签名链。每位所有者通过对上一笔交易的哈希和下一位所有者的公钥进行数字签名,并将这些内容添加到这枚币的末尾,从而将其转交给下一位所有者。收款人可以通过验证签名来核实所有权链。
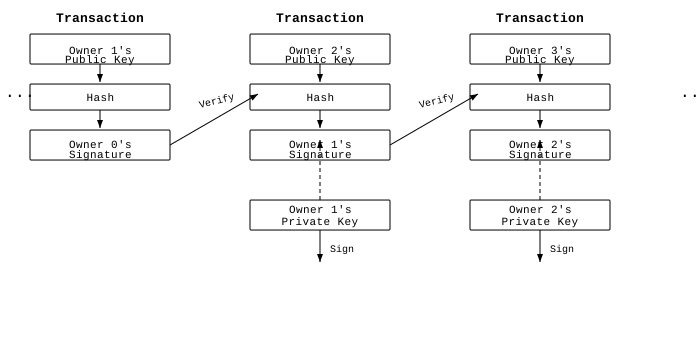
问题当然在于,收款人无法验证某位所有者没有对这枚币进行双重支付。常见的解决办法是引入一个可信的中央机构,也就是铸币机构,由它检查每笔交易是否存在双重支付。每笔交易之后,必须将币交回铸币机构,由其发行一枚新币;只有铸币机构直接发行的币才被信任为未被双重支付。这一方案的问题在于,整个货币系统的命运都取决于运营铸币机构的公司,每笔交易都必须经过它,就像银行一样。
我们需要一种方法,让收款人知道先前的所有者没有签署过任何更早的交易。就我们的目的而言,最早的交易才算数,因此我们不关心之后的双重支付尝试。确认一笔交易不存在的唯一办法,是知晓所有交易。在基于铸币机构的模式中,铸币机构知晓所有交易,并决定哪一笔最先到达。要在没有可信第三方的情况下做到这一点,交易必须公开宣布 [1],而且我们需要一个系统,使参与者就交易接收顺序的唯一历史达成一致。收款人需要证明,在每笔交易发生时,多数节点都同意它是最先收到的那一笔。
3. 时间戳服务器
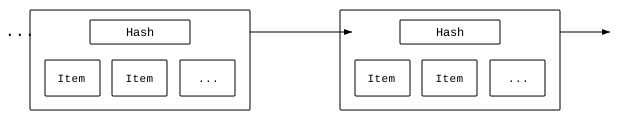
我们提出的解决方案从时间戳服务器开始。时间戳服务器的工作方式是,对一组需要加时间戳的项目所组成的区块取哈希,并广泛公布该哈希,例如刊登在报纸或 Usenet 帖子中 [2-5]。显然,为了被纳入哈希,这些数据当时必然已经存在,而时间戳证明了这一点。每个时间戳都将前一个时间戳包含在自己的哈希中,由此形成一条链;每增加一个时间戳,都会进一步强化此前的时间戳。
4. 工作量证明
为了以点对点方式实现分布式时间戳服务器,我们需要使用一种类似 Adam Back 的 Hashcash [6] 的工作量证明系统,而不是报纸或 Usenet 帖子。工作量证明需要搜索一个数值,使其经过哈希处理(例如使用 SHA-256)后,所得哈希以若干个零比特开头。所需的平均工作量会随要求的零比特数量呈指数增长,而验证时只需执行一次哈希运算。
对于我们的时间戳网络,我们通过不断递增区块中的 nonce 来实现工作量证明,直到找到一个能使区块哈希满足所需零比特数量的值。一旦为使区块满足工作量证明而投入了 CPU 算力,若不重做这些工作,该区块就无法更改。由于后续区块会链接在它后面,更改该区块所需的工作还包括重做它之后的所有区块。
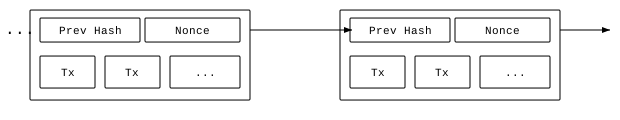
工作量证明还解决了多数决策中如何确定代表权的问题。如果多数取决于一个 IP 地址一票,那么任何能够分配大量 IP 地址的人都可以破坏这一机制。工作量证明本质上是一颗 CPU 一票。多数决定由最长链代表,因为其中投入的工作量证明工作最多。如果大部分 CPU 算力由诚实节点控制,诚实链就会增长得最快,并超越所有竞争链。要修改过去的某个区块,攻击者必须重做该区块及其后所有区块的工作量证明,然后追上并超过诚实节点完成的工作。我们稍后会证明,随着后续区块不断增加,速度较慢的攻击者追上的概率会呈指数下降。
5. 网络
运行网络的步骤如下:
- 新交易被广播至所有节点。
- 每个节点将新交易收集到一个区块中。
- 每个节点努力为自己的区块寻找一个高难度的工作量证明。
- 当某个节点找到工作量证明时,它会将该区块广播至所有节点。
- 只有当区块中的所有交易都有效且尚未被花费时,节点才接受该区块。
- 节点以被接受区块的哈希作为前一个哈希,着手创建链中的下一个区块,以此表示自己接受该区块。
节点始终将最长链视为正确的链,并会继续努力延长它。如果两个节点同时广播下一个区块的不同版本,一些节点可能先收到其中一个版本,另一些则先收到另一个。在这种情况下,它们会基于自己先收到的版本继续工作,但也会保存另一条分支,以防它变得更长。当下一个工作量证明被找到、其中一条分支变得更长时,平局便会打破;原本在另一条分支上工作的节点随后会切换到更长的那一条。
新交易的广播不一定需要到达所有节点。只要到达足够多的节点,它们很快就会被纳入某个区块。区块广播也能容忍消息丢失。如果某个节点没有收到一个区块,它会在收到下一个区块并意识到自己漏掉一个区块时,请求获取该区块。
6. 激励
按照约定,区块中的第一笔交易是一笔特殊交易,它会生成一枚由该区块创建者拥有的新币。这为节点支持网络增添了激励,也提供了一种最初将币分发进入流通的方法,因为没有中央机构来发行它们。以恒定数量持续增加新币,类似于金矿工人耗费资源,把黄金加入流通。在我们的情形中,所耗费的是 CPU 时间和电力。
激励也可能有助于鼓励节点保持诚实。如果贪婪的攻击者能够集结比所有诚实节点更多的 CPU 算力,他就必须在两者之间作出选择:用这些算力通过窃回自己的付款来欺骗人们,或是用它来生成新币。与破坏系统及其自身财富的有效性相比,他理应发现遵守规则更有利可图,因为这些规则让他获得的新币比其他所有人加起来还要多。
为了补偿硬件速度不断提升以及人们运行节点的兴趣随时间变化,工作量证明难度由移动平均值决定,其目标是达到每小时平均生成一定数量的区块。如果区块生成得太快,难度就会提高。
7. 回收磁盘空间
一旦一枚币的最新交易被足够多的区块掩埋,就可以丢弃它之前已经花费的交易,以节省磁盘空间。为了在不破坏区块哈希的情况下实现这一点,交易被哈希进一棵 Merkle 树 [7][2][5],只有树根被纳入区块哈希。随后可以通过截去树的分支来压缩旧区块。内部哈希无需存储。
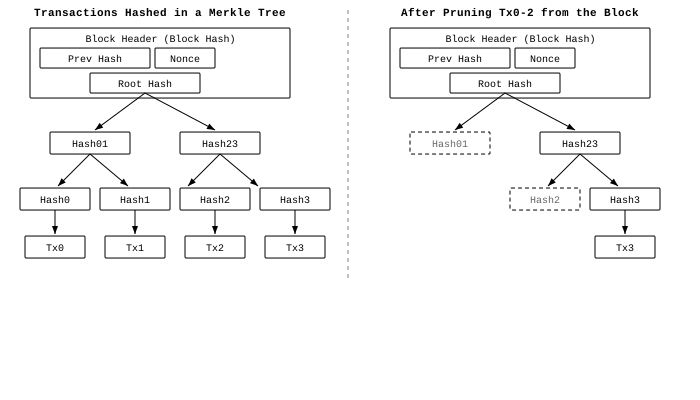
一个不含交易的区块头大约为 80 字节。如果假设每 10 分钟生成一个区块,那么每年为 80 字节 * 6 * 24 * 365 = 4.2MB。以 2008 年的情况来看,市售计算机系统通常配有 2GB 内存,而摩尔定律预测当前每年增长 1.2GB,因此即使区块头必须保存在内存中,存储也不应成为问题。
8. 简化支付验证
无需运行完整的网络节点也可以验证支付。用户只需保存最长工作量证明链的区块头副本;他可以不断查询网络节点,直到确信自己拥有最长链,并获取一条将交易链接到为其加时间戳的区块的 Merkle 分支。他无法亲自检查交易,但通过将交易链接到链中的某个位置,他可以看到某个网络节点已经接受了它,而其后新增的区块则进一步确认网络已经接受它。
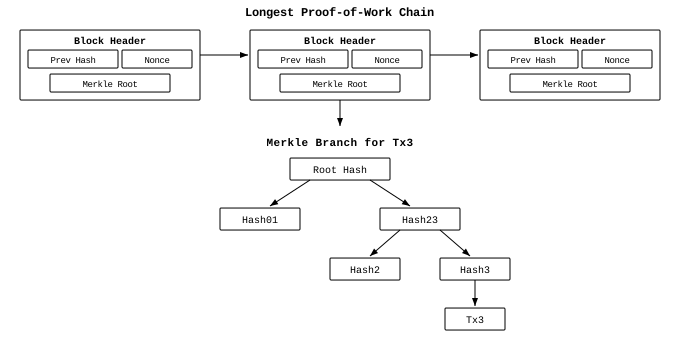
因此,只要诚实节点控制着网络,这种验证就是可靠的;但如果攻击者以更强算力压倒网络,它就更容易受到攻击。网络节点能够自行验证交易,并且只容易受到交易逆转的影响;而只要攻击者能继续以更强算力压倒网络,简化方法就可能被攻击者伪造的交易所欺骗。一种防护策略是,在网络节点检测到无效区块时接收它们发出的警报,促使用户的软件下载完整区块和被报告的交易,以确认不一致之处。频繁接收付款的企业可能仍会希望运行自己的节点,以获得更独立的安全保障和更快的验证。
9. 价值的合并与拆分
虽然可以逐枚处理币,但一次转账中的每一分钱都单独进行一笔交易会非常笨重。为了使价值能够拆分和合并,交易包含多个输入和输出。通常,要么是来自一笔金额较大的先前交易的单个输入,要么是由多个较小金额合并而成的多个输入;输出最多有两个:一个用于付款,另一个用于将找零(如果有)退回给发送者。
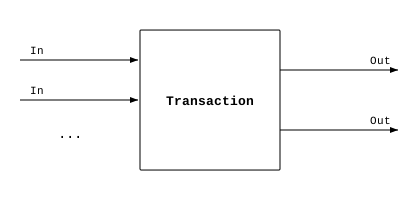
需要注意的是,扇出在这里不是问题;所谓扇出,是指一笔交易依赖于若干笔交易,而这些交易又依赖于更多交易。永远不需要提取一笔交易历史的完整独立副本。
10. 隐私
传统银行模式通过将信息访问权限限制在相关参与方和可信第三方之内,实现一定程度的隐私。必须公开宣布所有交易,使这种方法无法采用;但仍然可以通过在另一处切断信息流来保护隐私:让公钥保持匿名。公众可以看到某人正向另一个人发送一笔金额,却没有信息能将这笔交易与任何人联系起来。这类似于证券交易所公布的信息水平:每笔交易的时间和规模,也就是“行情记录”,会被公开,但不会说明参与方是谁。
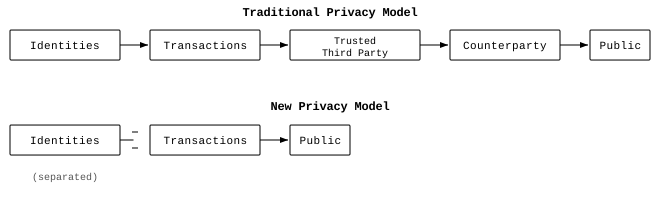
作为一道额外的防火墙,每笔交易都应使用一对新的密钥,以免它们被关联到同一个所有者。在多输入交易中,某些关联仍不可避免,因为这类交易必然会揭示其输入由同一个所有者拥有。风险在于,如果某个密钥的所有者身份被揭示,这种关联可能会揭示属于同一所有者的其他交易。
11. 计算
我们考虑这样一种情形:攻击者试图以快于诚实链的速度生成一条替代链。即使他做到了,也不会让系统任由随意更改,例如凭空创造价值,或拿走从未属于攻击者的钱。节点不会接受无效交易作为付款,诚实节点也绝不会接受包含无效交易的区块。攻击者只能尝试更改自己的某笔交易,以收回自己最近花掉的钱。
诚实链与攻击者链之间的竞赛,可以描述为二项随机游走。成功事件是诚实链延长一个区块,使其领先优势增加 +1;失败事件是攻击者链延长一个区块,使差距减少 -1。
攻击者从给定落后差距追上的概率,类似于赌徒破产问题。假设一名拥有无限信用的赌徒从落后状态开始,可能进行无限次尝试,试图达到盈亏平衡。我们可以如下计算他最终达到盈亏平衡的概率,也就是攻击者最终追上诚实链的概率 [8]:
- p = 诚实节点找到下一个区块的概率
- q = 攻击者找到下一个区块的概率
- qz = 攻击者从落后 z 个区块的状态最终追上的概率
根据我们对 p > q 的假设,随着攻击者必须追赶的区块数量增加,概率会呈指数下降。形势对他不利;如果他没有在早期幸运地向前猛冲,随着落后得越来越多,他的机会将变得微乎其微。
转换为 C 代码:
#include <math.h>
double AttackerSuccessProbability(double q, int z)
{
    double p = 1.0 - q;
    double lambda = z * (q / p);
    double sum = 1.0;
    int i, k;
    for (k = 0; k <= z; k++)
    {
        double poisson = exp(-lambda);
        for (i = 1; i <= k; i++)
            poisson *= lambda / i;
        sum -= poisson * (1 - pow(q / p, z - k));
    }
    return sum;
}
运行一些结果后,可以看到概率随着 z 呈指数下降。
q=0.1
z=0    P=1.0000000
z=1    P=0.2045873
z=2    P=0.0509779
z=3    P=0.0131722
z=4    P=0.0034552
z=5    P=0.0009137
z=6    P=0.0002428
z=7    P=0.0000647
z=8    P=0.0000173
z=9    P=0.0000046
z=10   P=0.0000012

q=0.3
z=0    P=1.0000000
z=5    P=0.1773523
z=10   P=0.0416605
z=15   P=0.0101008
z=20   P=0.0024804
z=25   P=0.0006132
z=30   P=0.0001522
z=35   P=0.0000379
z=40   P=0.0000095
z=45   P=0.0000024
z=50   P=0.0000006
求解 P 小于 0.1% 的情况……
P < 0.001
q=0.10   z=5
q=0.15   z=8
q=0.20   z=11
q=0.25   z=15
q=0.30   z=24
q=0.35   z=41
q=0.40   z=89
q=0.45   z=340
12. 结论
我们提出了一个无需依赖信任的电子交易系统。我们从由数字签名构成币的常规框架出发,它能对所有权提供有力控制,但若没有防止双重支付的方法,这个框架并不完整。为了解决这一问题,我们提出使用工作量证明的点对点网络来记录公开的交易历史;如果诚实节点控制着大部分 CPU 算力,那么攻击者很快就会在计算上难以更改这段历史。该网络因其无结构的简洁性而稳健。所有节点同时工作,只需极少协调。它们无需表明身份,因为消息不会被路由到任何特定地点,只需以尽力而为的方式传递即可。节点可以随时离开和重新加入网络,并将工作量证明链视为自己离线期间所发生事件的证明。它们用 CPU 算力投票:通过着手延长有效区块来表示接受它们,通过拒绝在无效区块上工作来表示拒绝它们。任何必要的规则和激励都可以通过这一共识机制来执行。
参考文献
[1] W. Dai,《b-money》,http://www.weidai.com/bmoney.txt,1998 年。
[2] H. Massias、X.S. Avila 和 J.-J. Quisquater,《最低信任要求下安全时间戳服务的设计》,载于第 20 届比荷卢信息论研讨会,1999 年 5 月。
[3] S. Haber、W.S. Stornetta,《如何为数字文档加时间戳》,载于《密码学杂志》,第 3 卷第 2 期,第 99-111 页,1991 年。
[4] D. Bayer、S. Haber、W.S. Stornetta,《提高数字时间戳的效率与可靠性》,载于《序列 II:通信、安全与计算机科学方法》,第 329-334 页,1993 年。
[5] S. Haber、W.S. Stornetta,《比特串的安全名称》,载于第 4 届 ACM 计算机与通信安全会议论文集,第 28-35 页,1997 年 4 月。
[6] A. Back,《Hashcash——一种拒绝服务对策》,http://www.hashcash.org/papers/hashcash.pdf,2002 年。
[7] R.C. Merkle,《公钥密码系统协议》,载于 1980 年安全与隐私研讨会论文集,IEEE 计算机学会,第 122-133 页,1980 年 4 月。
[8] W. Feller,《概率论及其应用导论》,1957 年。
英文原文
展开英文原文
Bitcoin: A Peer-to-Peer Electronic Cash System
Satoshi Nakamoto
www.bitcoin.org
Abstract. A purely peer-to-peer version of electronic cash would allow online payments to be sent directly from one party to another without the burdens of going through a financial institution. Digital signatures provide part of the solution, but the main benefits are lost if a trusted party is still required to prevent double-spending. We propose a solution to the double-spending problem using a peer-to-peer network. The network timestamps transactions by hashing them into an ongoing chain of hash-based proof-of-work, forming a record that cannot be changed without redoing the proof-of-work. The longest chain not only serves as proof of the sequence of events witnessed, but proof that it came from the largest pool of CPU power. As long as honest nodes control the most CPU power on the network, they can generate the longest chain and outpace any attackers. The network itself requires minimal structure. Messages are broadcasted on a best effort basis, and nodes can leave and rejoin the network at will, accepting the longest proof-of-work chain as proof of what happened while they were gone.
1. Introduction
Commerce on the Internet has come to rely almost exclusively on financial institutions serving as trusted third parties to process electronic payments. While the system works well enough for most transactions, it still suffers from the inherent weaknesses of the trust based model. Completely non-reversible transactions are not really possible, since financial institutions cannot avoid mediating disputes. The cost of mediation increases transaction costs, limiting the minimum practical transaction size and cutting off the possibility for small casual transactions, and there is a broader cost in the loss of ability to make non-reversible payments for non-reversible services. With the possibility of reversal, the need for trust spreads. Merchants must be wary of their customers, hassling them for more information than they would otherwise need. A certain percentage of fraud is accepted as unavoidable. These costs and payment uncertainties can be avoided in person by using physical currency, but no mechanism exists to make payments over a communications channel without a trusted party.
What is needed is an electronic payment system based on cryptographic proof instead of trust, allowing any two willing parties to transact directly with each other without the need for a trusted third party. Transactions that are computationally impractical to reverse would protect sellers from fraud, and routine escrow mechanisms could easily be implemented to protect buyers. In this paper, we propose a solution to the double-spending problem using a peer-to-peer distributed timestamp server to generate computational proof of the chronological order of transactions. The system is secure as long as honest nodes collectively control more CPU power than any cooperating group of attacker nodes.
2. Transactions
We define an electronic coin as a chain of digital signatures. Each owner transfers the coin to the next by digitally signing a hash of the previous transaction and the public key of the next owner and adding these to the end of the coin. A payee can verify the signatures to verify the chain of ownership.
The problem of course is the payee can't verify that one of the owners did not double-spend the coin. A common solution is to introduce a trusted central authority, or mint, that checks every transaction for double spending. After each transaction, the coin must be returned to the mint to issue a new coin, and only coins issued directly from the mint are trusted not to be double-spent. The problem with this solution is that the fate of the entire money system depends on the company running the mint, with every transaction having to go through them, just like a bank.
We need a way for the payee to know that the previous owners did not sign any earlier transactions. For our purposes, the earliest transaction is the one that counts, so we don't care about later attempts to double-spend. The only way to confirm the absence of a transaction is to be aware of all transactions. In the mint based model, the mint was aware of all transactions and decided which arrived first. To accomplish this without a trusted party, transactions must be publicly announced [1], and we need a system for participants to agree on a single history of the order in which they were received. The payee needs proof that at the time of each transaction, the majority of nodes agreed it was the first received.
3. Timestamp Server
The solution we propose begins with a timestamp server. A timestamp server works by taking a hash of a block of items to be timestamped and widely publishing the hash, such as in a newspaper or Usenet post [2-5]. The timestamp proves that the data must have existed at the time, obviously, in order to get into the hash. Each timestamp includes the previous timestamp in its hash, forming a chain, with each additional timestamp reinforcing the ones before it.
4. Proof-of-Work
To implement a distributed timestamp server on a peer-to-peer basis, we will need to use a proof-of-work system similar to Adam Back's Hashcash [6], rather than newspaper or Usenet posts. The proof-of-work involves scanning for a value that when hashed, such as with SHA-256, the hash begins with a number of zero bits. The average work required is exponential in the number of zero bits required and can be verified by executing a single hash.
For our timestamp network, we implement the proof-of-work by incrementing a nonce in the block until a value is found that gives the block's hash the required zero bits. Once the CPU effort has been expended to make it satisfy the proof-of-work, the block cannot be changed without redoing the work. As later blocks are chained after it, the work to change the block would include redoing all the blocks after it.
The proof-of-work also solves the problem of determining representation in majority decision making. If the majority were based on one-IP-address-one-vote, it could be subverted by anyone able to allocate many IPs. Proof-of-work is essentially one-CPU-one-vote. The majority decision is represented by the longest chain, which has the greatest proof-of-work effort invested in it. If a majority of CPU power is controlled by honest nodes, the honest chain will grow the fastest and outpace any competing chains. To modify a past block, an attacker would have to redo the proof-of-work of the block and all blocks after it and then catch up with and surpass the work of the honest nodes. We will show later that the probability of a slower attacker catching up diminishes exponentially as subsequent blocks are added.
5. Network
The steps to run the network are as follows:
- New transactions are broadcasted to all nodes.
- Each node collects new transactions into a block.
- Each node works on finding a difficult proof-of-work for its block.
- When a node finds a proof-of-work, it broadcasts the block to all nodes.
- Nodes accept the block only if all transactions in it are valid and not already spent.
- Nodes express their acceptance of the block by working on creating the next block in the chain, using the hash of the accepted block as the previous hash.
Nodes always consider the longest chain to be the correct one and will keep working on extending it. If two nodes broadcast different versions of the next block simultaneously, some nodes may receive one or the other first. In that case, they work on the first one they received, but save the other branch in case it becomes longer. The tie will be broken when the next proof-of-work is found and one branch becomes longer; the nodes that were working on the other branch will then switch to the longer one.
New transaction broadcasts do not necessarily need to reach all nodes. As long as they reach many nodes, they will get into a block before long. Block broadcasts are also tolerant of dropped messages. If a node does not receive a block, it will request it when it receives the next block and realizes it missed one.
6. Incentive
By convention, the first transaction in a block is a special transaction that starts a new coin owned by the creator of the block. This adds an incentive for nodes to support the network, and provides a way to initially distribute coins into circulation, since there is no central authority to issue them. The steady addition of a constant of amount of new coins is analogous to gold miners expending resources to add gold to circulation. In our case, it is CPU time and electricity that is expended.
The incentive may also help encourage nodes to stay honest. If a greedy attacker is able to assemble more CPU power than all the honest nodes, he would have to choose between using it to defraud people by stealing back his payments, or using it to generate new coins. He ought to find it more profitable to play by the rules, such rules that favour him with more new coins than everyone else combined, than to undermine the system and the validity of his own wealth.
To compensate for increasing hardware speed and varying interest in running nodes over time, the proof-of-work difficulty is determined by a moving average targeting an average number of blocks per hour. If they're generated too fast, the difficulty increases.
7. Reclaiming Disk Space
Once the latest transaction in a coin is buried under enough blocks, the spent transactions before it can be discarded to save disk space. To facilitate this without breaking the block's hash, transactions are hashed in a Merkle Tree [7][2][5], with only the root included in the block's hash. Old blocks can then be compacted by stubbing off branches of the tree. The interior hashes do not need to be stored.
A block header with no transactions would be about 80 bytes. If we suppose blocks are generated every 10 minutes, 80 bytes * 6 * 24 * 365 = 4.2MB per year. With computer systems typically selling with 2GB of RAM as of 2008, and Moore's Law predicting current growth of 1.2GB per year, storage should not be a problem even if the block headers must be kept in memory.
8. Simplified Payment Verification
It is possible to verify payments without running a full network node. A user only needs to keep a copy of the block headers of the longest proof-of-work chain, which he can get by querying network nodes until he's convinced he has the longest chain, and obtain the Merkle branch linking the transaction to the block it's timestamped in. He can't check the transaction for himself, but by linking it to a place in the chain, he can see that a network node has accepted it, and blocks added after it further confirm the network has accepted it.
As such, the verification is reliable as long as honest nodes control the network, but is more vulnerable if the network is overpowered by an attacker. While network nodes can verify transactions for themselves and are only vulnerable to reversal, the simplified method can be fooled by an attacker's fabricated transactions for as long as the attacker can continue to overpower the network. One strategy to protect against this would be to accept alerts from network nodes when they detect an invalid block, prompting the user's software to download the full block and reported transactions to confirm the inconsistency. Businesses that receive frequent payments will probably still want to run their own nodes for more independent security and quicker verification.
9. Combining and Splitting Value
Although it would be possible to handle coins individually, it would be unwieldy to make a separate transaction for every cent in a transfer. To allow value to be split and combined, transactions contain multiple inputs and outputs. Normally there will be either a single input from a larger previous transaction or multiple inputs combining smaller amounts, and at most two outputs: one for the payment, and one returning the change, if any, back to the sender.
It should be noted that fan-out, where a transaction depends on several transactions, and those transactions depend on many more, is not a problem here. There is never the need to extract a complete standalone copy of a transaction's history.
10. Privacy
The traditional banking model achieves a level of privacy by limiting access to information to the parties involved and the trusted third party. The necessity to announce all transactions publicly precludes this method, but privacy can still be maintained by breaking the flow of information in another place: by keeping public keys anonymous. The public can see that someone is sending an amount to someone else, but without information linking the transaction to anyone. This is similar to the level of information released by stock exchanges, where the time and size of individual trades, the "tape", is made public, but without telling who the parties were.
As an additional firewall, a new key pair should be used for each transaction to keep them from being linked to a common owner. Some linking is still unavoidable with multi-input transactions, which necessarily reveal that their inputs were owned by the same owner. The risk is that if the owner of a key is revealed, linking could reveal other transactions that belonged to the same owner.
11. Calculations
We consider the scenario of an attacker trying to generate an alternate chain faster than the honest chain. Even if this is accomplished, it does not throw the system open to arbitrary changes, such as creating value out of thin air or taking money that never belonged to the attacker. Nodes are not going to accept an invalid transaction as payment, and honest nodes will never accept a block containing them. An attacker can only try to change one of his own transactions to take back money he recently spent.
The race between the honest chain and an attacker chain can be characterized as a Binomial Random Walk. The success event is the honest chain being extended by one block, increasing its lead by +1, and the failure event is the attacker's chain being extended by one block, reducing the gap by -1.
The probability of an attacker catching up from a given deficit is analogous to a Gambler's Ruin problem. Suppose a gambler with unlimited credit starts at a deficit and plays potentially an infinite number of trials to try to reach breakeven. We can calculate the probability he ever reaches breakeven, or that an attacker ever catches up with the honest chain, as follows [8]:
- p = probability an honest node finds the next block
- q = probability the attacker finds the next block
- qz = probability the attacker will ever catch up from z blocks behind
Given our assumption that p > q, the probability drops exponentially as the number of blocks the attacker has to catch up with increases. With the odds against him, if he doesn't make a lucky lunge forward early on, his chances become vanishingly small as he falls further behind.
Converting to C code:
#include <math.h>
double AttackerSuccessProbability(double q, int z)
{
    double p = 1.0 - q;
    double lambda = z * (q / p);
    double sum = 1.0;
    int i, k;
    for (k = 0; k <= z; k++)
    {
        double poisson = exp(-lambda);
        for (i = 1; i <= k; i++)
            poisson *= lambda / i;
        sum -= poisson * (1 - pow(q / p, z - k));
    }
    return sum;
}
Running some results, we can see the probability drop off exponentially with z.
q=0.1
z=0    P=1.0000000
z=1    P=0.2045873
z=2    P=0.0509779
z=3    P=0.0131722
z=4    P=0.0034552
z=5    P=0.0009137
z=6    P=0.0002428
z=7    P=0.0000647
z=8    P=0.0000173
z=9    P=0.0000046
z=10   P=0.0000012

q=0.3
z=0    P=1.0000000
z=5    P=0.1773523
z=10   P=0.0416605
z=15   P=0.0101008
z=20   P=0.0024804
z=25   P=0.0006132
z=30   P=0.0001522
z=35   P=0.0000379
z=40   P=0.0000095
z=45   P=0.0000024
z=50   P=0.0000006
Solving for P less than 0.1%...
P < 0.001
q=0.10   z=5
q=0.15   z=8
q=0.20   z=11
q=0.25   z=15
q=0.30   z=24
q=0.35   z=41
q=0.40   z=89
q=0.45   z=340
12. Conclusion
We have proposed a system for electronic transactions without relying on trust. We started with the usual framework of coins made from digital signatures, which provides strong control of ownership, but is incomplete without a way to prevent double-spending. To solve this, we proposed a peer-to-peer network using proof-of-work to record a public history of transactions that quickly becomes computationally impractical for an attacker to change if honest nodes control a majority of CPU power. The network is robust in its unstructured simplicity. Nodes work all at once with little coordination. They do not need to be identified, since messages are not routed to any particular place and only need to be delivered on a best effort basis. Nodes can leave and rejoin the network at will, accepting the proof-of-work chain as proof of what happened while they were gone. They vote with their CPU power, expressing their acceptance of valid blocks by working on extending them and rejecting invalid blocks by refusing to work on them. Any needed rules and incentives can be enforced with this consensus mechanism.
References
[1] W. Dai, "b-money," http://www.weidai.com/bmoney.txt, 1998.
[2] H. Massias, X.S. Avila, and J.-J. Quisquater, "Design of a secure timestamping service with minimal trust requirements," In 20th Symposium on Information Theory in the Benelux, May 1999.
[3] S. Haber, W.S. Stornetta, "How to time-stamp a digital document," In Journal of Cryptology, vol 3, no 2, pages 99-111, 1991.
[4] D. Bayer, S. Haber, W.S. Stornetta, "Improving the efficiency and reliability of digital time-stamping," In Sequences II: Methods in Communication, Security and Computer Science, pages 329-334, 1993.
[5] S. Haber, W.S. Stornetta, "Secure names for bit-strings," In Proceedings of the 4th ACM Conference on Computer and Communications Security, pages 28-35, April 1997.
[6] A. Back, "Hashcash - a denial of service counter-measure," http://www.hashcash.org/papers/hashcash.pdf, 2002.
[7] R.C. Merkle, "Protocols for public key cryptosystems," In Proc. 1980 Symposium on Security and Privacy, IEEE Computer Society, pages 122-133, April 1980.
[8] W. Feller, "An introduction to probability theory and its applications," 1957.